Recommended Containers
Container options recommended by Game Warden to simplify onboarding and increase the likelihood of security approval.
For containerized applications, Game Warden recommends the following options to simplify onboarding and increase the likelihood of security approval:
Chainguard containers
Chainguard provides minimal, security-focused container images designed to reduce vulnerabilities and simplify compliance.
These images are typically smaller and less complex, often resulting in zero Common Vulnerabilities and Exposures (CVEs).
- Minimal footprint with a strong security posture.
- Often CVE-free, reducing your remediation burden.
- Free when using images tagged
latest.
Usage guidelines
-
You may build upon Chainguard base images and push your derived images to the Game Warden Harbor registry.
-
The
latesttag always pulls the newest image version, which may introduce unexpected changes. To avoid unexpected changes, always:- Pull the
latesttag. - Retag the image with your specific application version.
- Push the tagged version to Game Warden.
- Pull the
-
Chainguard images with tags other than
latestmay require a paid subscription. Contact your Mission Success Manager (MSM) for partnership details.
Iron Bank containers
Iron Bank hosts hardened container images vetted by Platform One (P1) to meet Department of War (DOW) standards. You can push these images to the Harbor registry and deploy them to Game Warden.
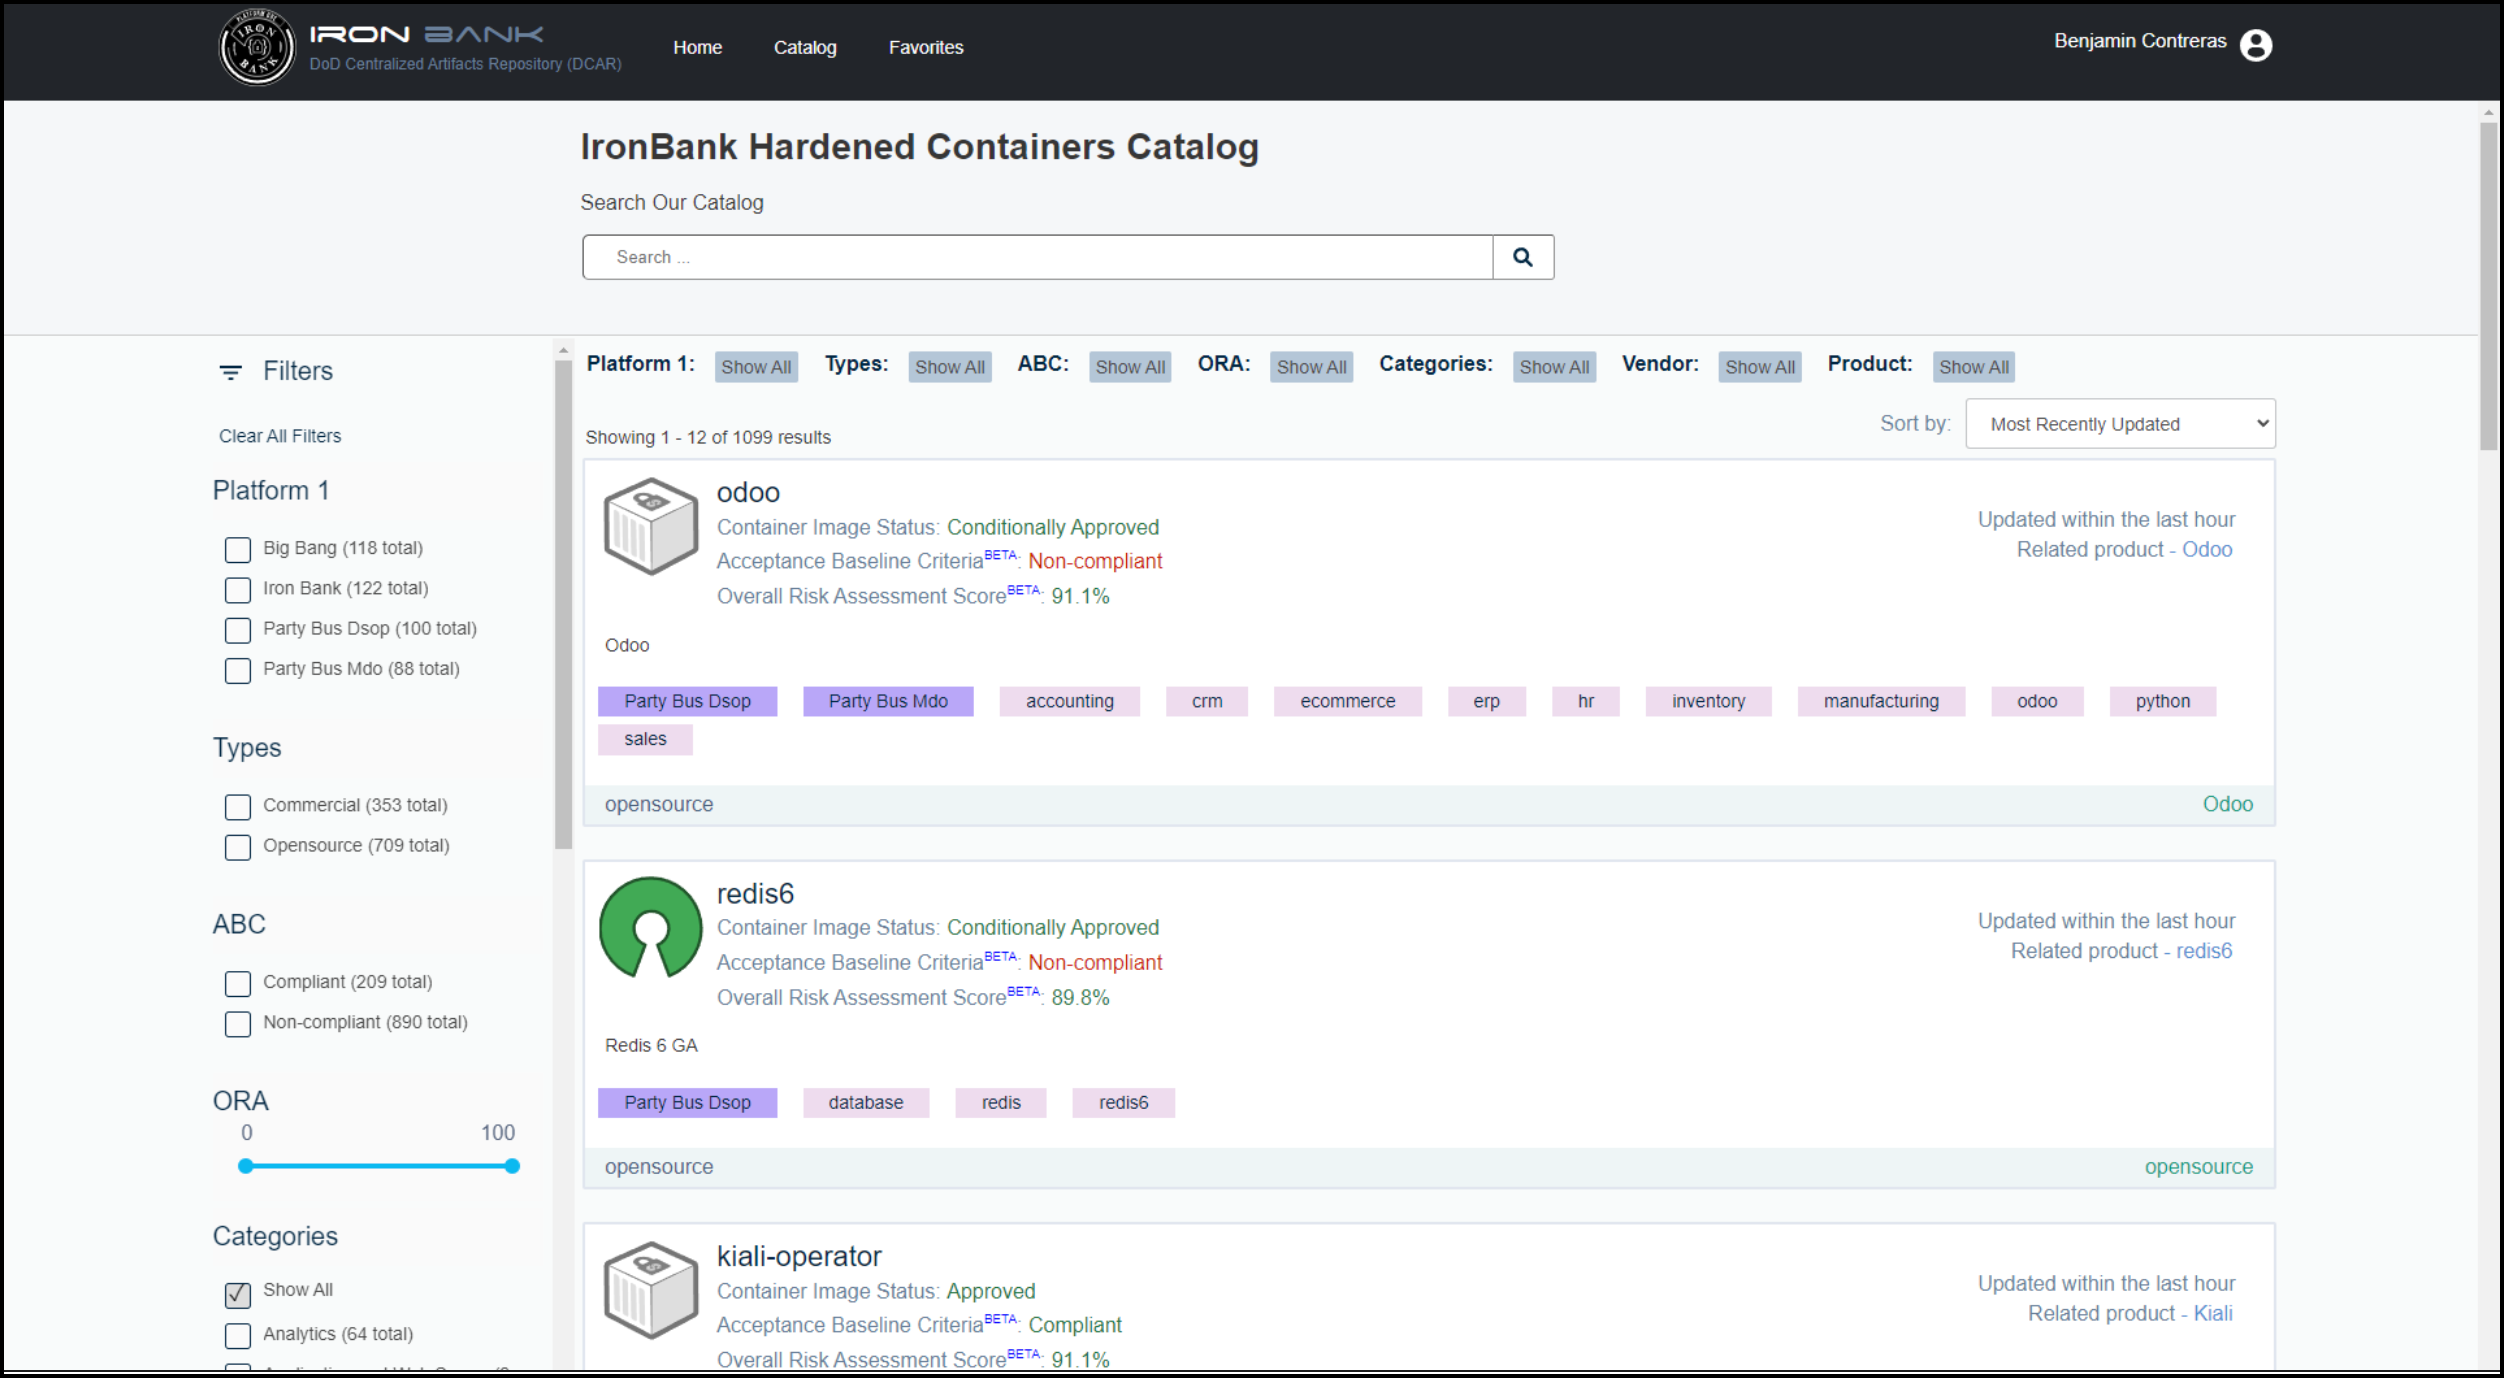
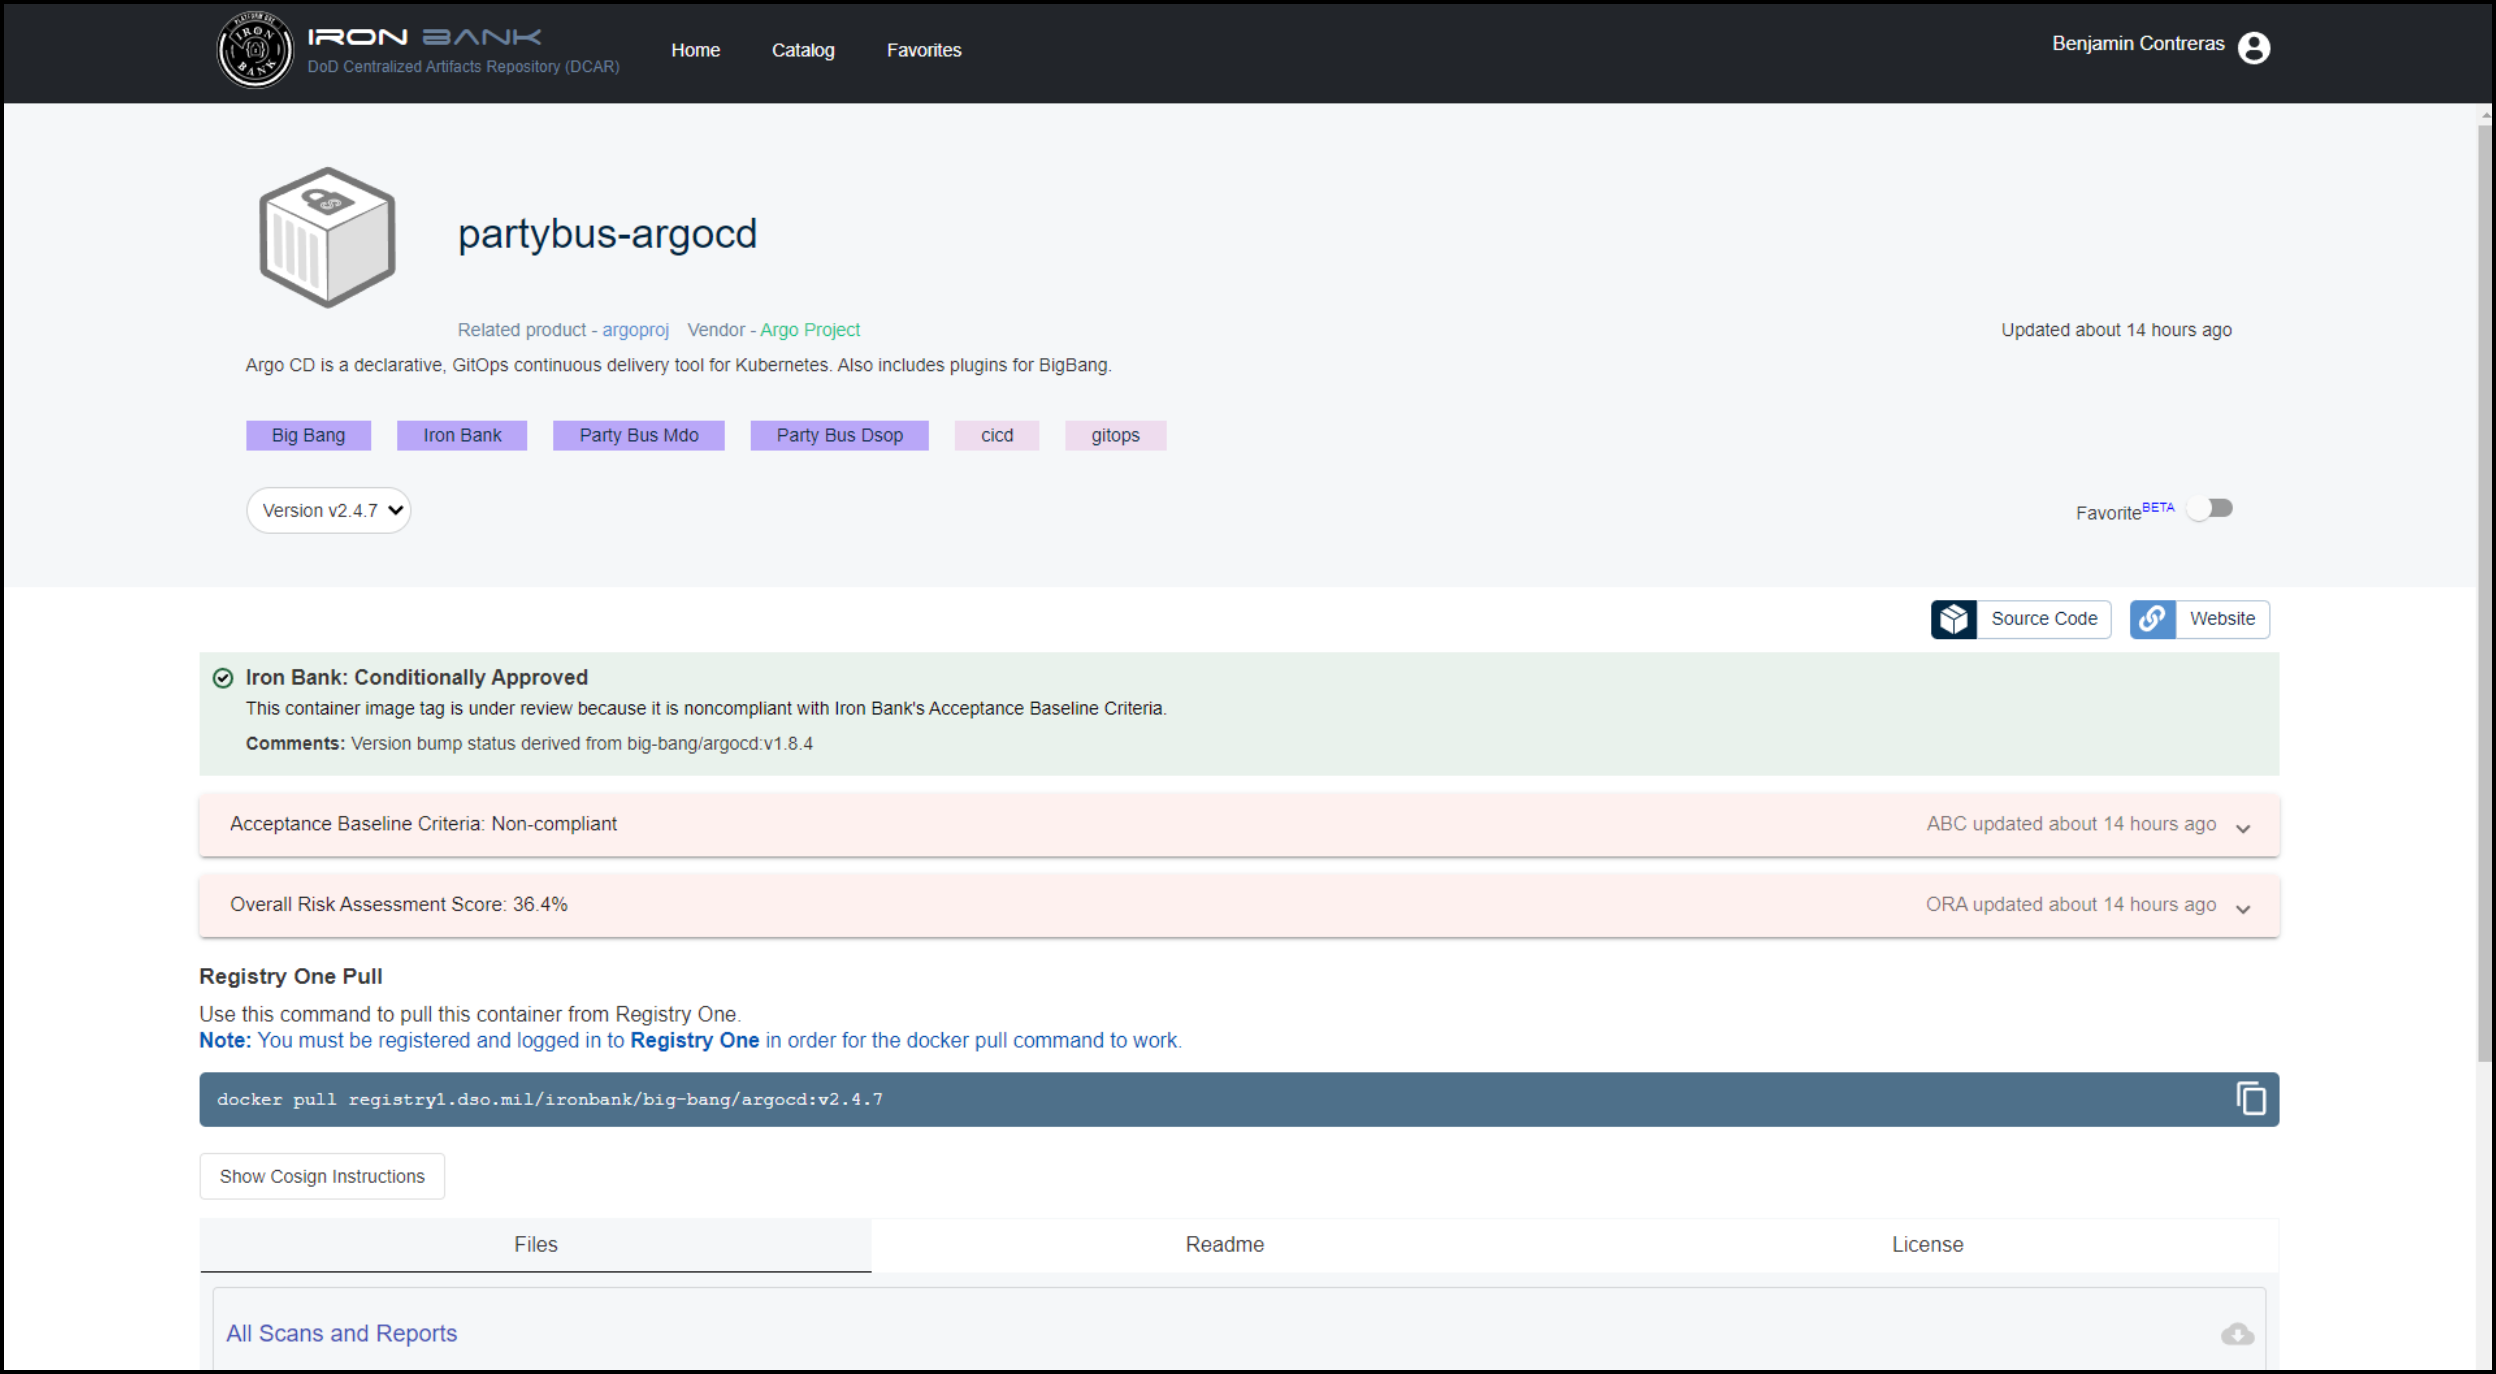
When selecting images from Iron Bank, pay close attention to two key ratings to assess the security posture of each image:
- Acceptance Baseline Criteria (ABC) - Indicates whether the image meets Iron Bank's security compliance standards.
- Overall Risk Assessment (ORA) - Scored between 0% and 100%, where higher scores reflect better security posture.
Choose images that are ABC Compliant with an ORA of 80% or higher to improve your chances of approval on the 2F platform.
Responsibilities when using Iron Bank
- Understand the ABC and ORA scores of your selected images.
- Notify the Game Warden team when you plan to use Iron Bank images with compliant status and strong ORA scores.
- Review image compliance and stay informed about End of Life (EoL) status because image compliance can change over time.
- If a container's compliance status changes:
- Coordinate with the image owner through P1 to resolve issues.
- Migrate to a compliant image if necessary.
- Always use the latest, compliant version of your selected image.
If an Iron Bank container does not initially meet security requirements, the Game Warden team may require you to choose a different image.
- Justify Low and Medium CVEs that exceed the approved thresholds.
- The security ream assessesHigh and Critical CVEs individually based on their security impact.
To avoid approval delays, notify the Game Warden team when selecting images for deployment.
- EoL images are unsupported and likely won't pass security review.
- Typically, you'll have 6–12 months of overlap between new and deprecated images.
- Check for updates monthly to maintain compliance.
How to pull from Iron Bank
Other container options
You may choose to build your own containers or select images outside of Chainguard or Iron Bank. These images will undergo more rigorous security scrutiny.
If you do, scan your images with open-source tools such as Trivy or Grype to identify and address Common Vulnerabilities and Exposures (CVEs) before submitting to Game Warden.
Recommended practice: Distroless containers
Distroless containers are minimal container images that include only the application and its runtime dependencies, they exclude the operating system package manager and unnecessary libraries. This approach improves security by reducing the container's attack surface and limits the potential for vulnerabilities.
- Smaller image size, leading to faster downloads and deployments.
- Fewer included libraries and tools, reducing the attack surface.
- Lower CVE exposure due to minimal dependencies.
- Easier to maintain and deploy consistently.