The 2F Platform Architecture
Overview of the 2F Platform's architectural components including infrastructure, security, and observability layers.
The 2F Platform provides a secure, scalable, and compliant environment for deploying SaaS applications to government networks. With built-in Authority to Operate (ATO) inheritance, observability, and CI/CD integration, the platform minimizes operational overhead while maintaining strict security and compliance standards.
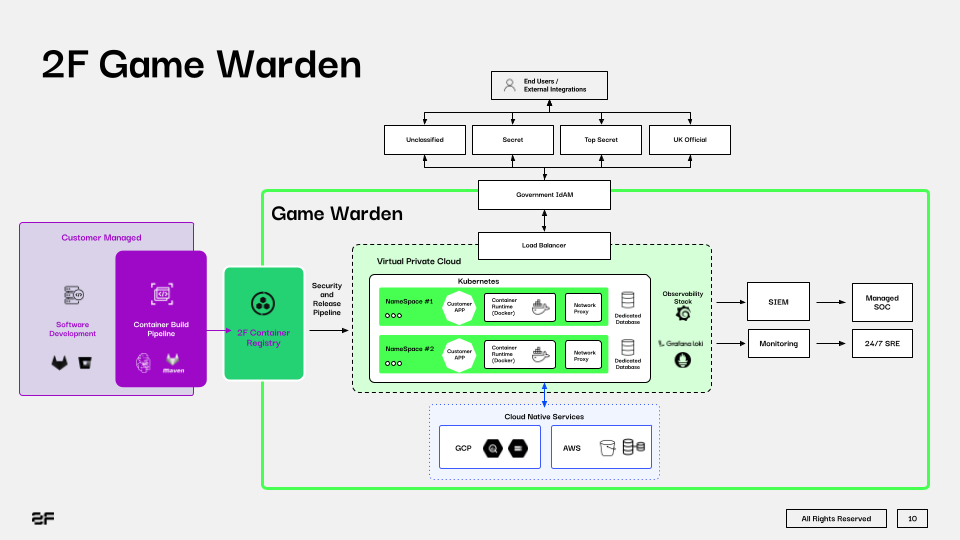
The following sections provide an overview of Game Warden's architectural components.
Customer-managed components
Your organization owns and operates the following components:
- Software development - Develop application code by using standard development tools and frameworks (for example, GitHub, GitLab, Bitbucket).
- Container build pipeline - Use a CI/CD pipeline managed by your organization to generate a Docker container image of your application's code.
Second Front container registry
Game Warden manages this secure registry to store validated application containers. The security and release pipeline processes these containers before deploying them to the 2F Platform.
The 2F Platform
The core platform hosts and manages the lifecycle of SaaS applications in a government-approved environment.
| Component | Description |
|---|---|
| Virtual Private Cloud (VPC) | The VPC serves as the isolated hosting environment where customer workloads run, ensuring network segmentation and policy enforcement. |
| Kubernetes Orchestration | Applications are deployed in dedicated namespaces, each containing:
|
| Cloud Native Services | Game Warden is cloud-agnostic and can run on multiple providers, including:
|
Security and compliance layer
Game Warden enforces strict access and compliance controls, including:
- Government IdAM & Load Balancer - All access to applications passes through a government-validated identity and access management system and a centralized load balancer.
- End User Access Tiers - Supports varying sensitivity levels: Unclassified, Secret, Top Secret, UK Official, etc., ensuring appropriate data segregation.
Observability and operations
Game Warden includes a built-in observability stack for operational insight and compliance monitoring:
- Grafana Loki - Used for application and system log aggregation.
- Monitoring Tools - Tracks performance, availability, and resource usage.
- SIEM Integration - Platform-level security event and information management for infrastructure monitoring and incident response.
- Managed SOC and every day SRE - Real-time security response and platform reliability support.